 STEALINT
Inside the computers of DPRK IT workers
On April 8, 2026, @ZachXBT published an investigation into North Korean overseas IT workers and how they manage payments with their home country. The breach originated from a compromised DPRK IT worker device infected by an infostealer, which provided access to internal communications via a payment reporting platform called luckyguys[.]site, allowing overseas workers to relay earnings back to their handlers.
The findings suggest a large-scale but relatively unsophisticated ecosystem of fraudulent remote IT work, generating significant revenue for North Korean networks. While less advanced than known operations like AppleJeus or TraderTraitor, this cluster highlights the breadth of DPRK cyber-enabled financial activity.
1/ Recently an unnamed source shared data exfiltrated from an internal North Korean payment server containing 390 accounts, chat logs, crypto transactions. I spent long hours going through all of it, none of which has ever been publicly released. It revealed an intricate... - @ZachXBT, April 8, 2026
Using the technical elements from Zach's findings, we were able to retrieve infostealer data associated with two DPRK workers from our STEALINT platform. Here is their story.
Key points
- The operation reflects a large-scale but relatively low-sophistication ecosystem of fraudulent remote IT work.
- Infostealers are not just threats - they are powerful cyberdefence tools for investigations. Infostealer telemetry can turn adversary compromise into actionable intelligence.
- DPRK IT worker operations rely on: VPN obfuscation with Astriil VPN, fake identities and portfolios, freelance and remote job platforms, and extended use of AI copilot tools during job interviews.
- They seem to be focused on the Middle-East region (Dubai and Saudi Arabia).
- Operators demonstrate moderate technical skills but strong operational scaling.
- Activities span beyond work: crypto, gambling and side-platform usage suggest diversified revenue channels or personal use.
Hero #1: Meet SuperDev
SuperDev was infected by an infostealer on March 15th 2026. He uses a Windows 11 OS installed in December 2025 with Korean-English language. His external IP was geolocated in the US, and associated with AstriilVPN, as mentioned by Zach.
Profiling the computer specs
From the list of the processes running on SuperDev's computer, we can assume he is running some kind of full-stack webdev work (code.exe, sublime_text.exe, node.exe, multiple postgres.exe). On the networking side, he has running instances of AstriilVPN - consistent with the observed external IP - and DeskIn, a remote desktop tool he probably used for remote work. SuperDev also uses Telegram, Slack, LibreOffice and Lightshot.
The list of installed software confirms what we saw from the running processes: tools like VisualStudio, Git, Postman and Android Studio, probably used for webdev. However, this list also reveals a data science and AI stack (Python, Anaconda) and an Exodus crypto wallet, QQPlayer and IP Messenger.
The diversity of tools shows that he is probably a flexible freelancer doing various development jobs. IP Messenger (Japanese), QQPlayer (Chinese) and AstriilVPN are mostly used in Asian countries.
As of yet, we cannot conclude that SuperDev is indeed from North Korea: elements from his computer specs only point to a regular Korean-speaking engineer searching for freelance dev work. But looking at his web accounts is where it gets truly interesting.
Looking at SuperDev's web accounts
Continuing to dig into the stealer data associated with SuperDev, we analyzed the 263 websites he saved credentials for. Two major patterns stand out: multiple URLs and logins showing that SuperDev has been developing several websites for clients, and several websites related to jobseeking platforms, fake personas and AI-based helpers for job interviews.
GitHub account. SuperDev owns the GitHub profile Perfectwork829, still active as of April 2026. Active since March 2023 with 30 repos, it shows several hallmarks of a fake or freelance-for-hire account.
- The most glaring red flag is the presence of three separate portfolio sites with different names -
amalPortfolio,oleksiiPorfolio,myportfolio- strongly suggesting the account is used to build fake GitHub credibility for multiple different people. - The sports betting theme appears four times (
sportsBetting,sports-betting-newversion,sports_betting_stepper, and a forked ML repo) - recycled work sold repeatedly, rather than genuine interest. - The technically noteworthy repos are
react-reduced-project(the only one showing awareness of modern tooling with Qwik and DaisyUI) and the Laravel suite, which at least demonstrates some backend breadth. - The brand-new
fullstack_dev_portfolioin Vue, created April 2026, fits the pattern of assembling yet another identity.
Overall, a profile built to look experienced rather than to document real development work.
Web development work. A major pattern is the abundance of local and staging URLs (localhost, 127.0.0.1, private IPs), indicating ongoing development, test environments and possibly multiple projects running in parallel. Figma previews and job/freelance platforms support the idea of a product-building or freelance workflow, combining development, design and client acquisition. For payments, SuperDev seems to mostly rely on PayPal and Stripe.
Jobseeking platforms and copilots. SuperDev has accounts on xing.com, SNAPHUNT (fldata.snaphunt.com), jobscan.com, myworkdayjobs.com, empleo.coremain.com, jobs.x-team.com, cybercoders.com and totaljobs.com. He also used several AI-powered copilot tools to boost his interviews: jobright.ai and ntro.io.
Other interesting findings. SuperDev also used virtual phone SMS providers such as SMSPool, and showed scattered activity on gambling, gaming and financial platforms:
- Gambling: bcgame.li, bcvn2.com, slotstemple.com
- Gaming: Roblox, Seafight, Xbox
- Trading / crypto / FOREX: xmtrading.com, xmglobal.com, mexc.com, okx.com, bitrue.com, mql5.com
SuperDev's multiple identities
New DPRK front found! Fake front company verityai[.]co. Fake accounts linked and boosted. 75% chance of being fake as well. - @Fox_threatintel, April 9, 2026
We can confirm that these allegations are correct and linked to our SuperDev guy. We can also add that SuperDev has worked on the following websites, according to stealer data: www.box12ksa.com and 3daysksa.com.
The first website is related to a likely fake gym; the second one seems to impersonate a real gym brand - both in Saudi Arabia. The fake X accounts associated with these websites are boosted by fake followers. Continuing our research, we found that both websites were advertising an APK associated with a company named Memvera on APKPure:
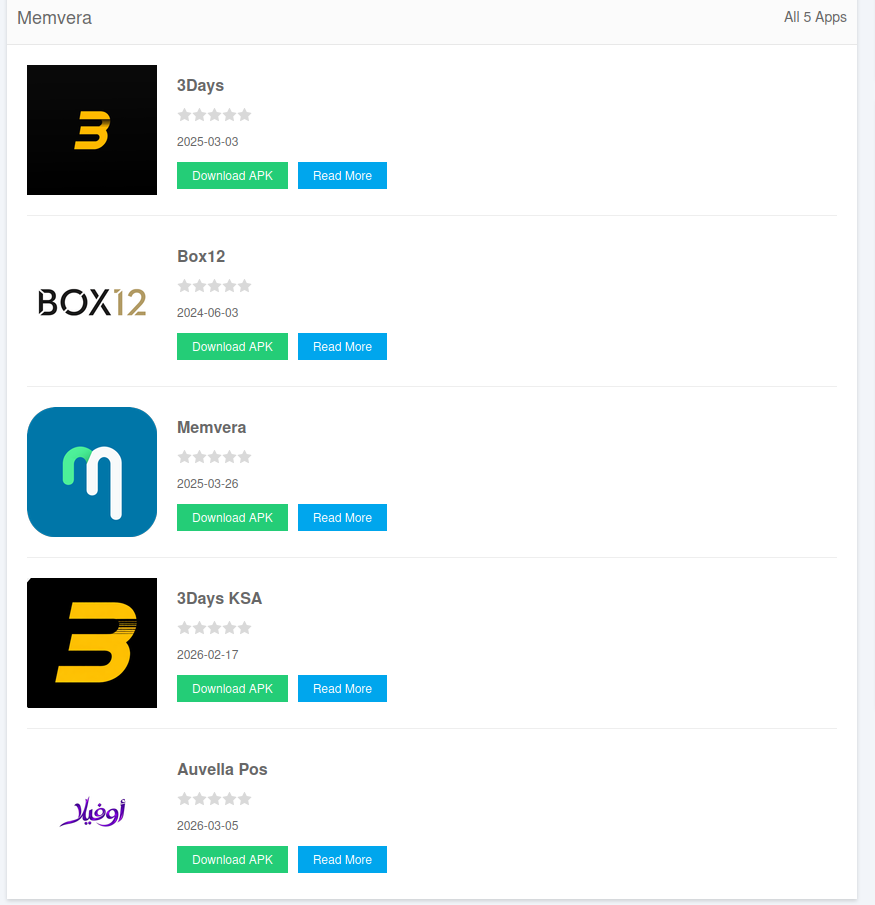
Memvera happens to be linked to the Shijazi88 persona mentioned in @Fox_threatintel's post: on the website shijazi.me, a person named Safwan Hijazi claims to be "CTO & Co-Founder @ ProMatrix / memvera". He seems to own the X account @shijazi88, which has the same handle as the GitHub account github.com/shijazi88.
This leads to three possibilities:
- Shijazi is a fake persona created by DPRK worker SuperDev to make money (highly likely)
- Shijazi and the Memvera company are impersonated by SuperDev (likely)
- Shijazi and Memvera hired SuperDev to develop their websites and APK (unlikely)
Hero #2: Meet DevWisdom
DevWisdom was infected with the Vidar stealer in late December 2025. His setup is quite similar to SuperDev's, with an external IP address located in Japan and associated with Astriil VPN ranges.
Computer specs
DevWisdom's running processes and installed software indicate a technically experienced user who primarily works with development tools and local environments. The presence of Node.js, Python and Git suggests regular involvement in programming - likely including backend development, scripting or automation. The use of both PostgreSQL and MongoDB indicates familiarity with different database systems and data models. The system also includes VMware Workstation, which points to the use of virtual machines for testing backend solutions.
Networking and remote access tools are also present. The user has Astriil VPN running - just like our SuperDev guy - showing that DPRK workers seem to consistently use this VPN, very popular in Asia. Additionally, AnyDesk indicates the user may access or manage systems remotely.
Overall, the environment is consistent with someone interested in web development, front and backend - very similar to SuperDev's profile.
DevWisdom's web accounts
Using stealer data, we found the personal fake portfolio of our suspect, where he claims to be a full-stack developer from Malaysia. On the website, we found a link to his GitHub handle: DevWisdom08.
GitHub account. DevWisdom08 is a recently created GitHub account (November 2025–February 2026) with 13 repositories spanning six languages - unusually broad for such a short timeframe, which raises questions about authenticity.
- The most structurally interesting work is the ISP SaaS suite - three separate repos (
isp-saas-platformin Go,isp-saas-frontendin Vue, andisp-agentin Go) that together suggest a full-stack product, withisp-agentbeing the only repo to have earned a star. - Football-Arena (Dart/Flutter) and rapresentante-commercianti (a Flutter loyalty-system MVP for local Italian merchants) stand out as the most concrete, domain-specific projects with actual descriptions.
- The AI-character-platform (TypeScript) and
movesbook-nextjsare the most recent additions and follow current market trends closely.
Overall, the profile reads less like an organic developer journey and more like a portfolio assembled quickly to appear credible - the lack of READMEs, descriptions and community engagement across most repos reinforces that impression.
Main pattern: job searching (tech-focused). A large portion of DevWisdom's account history is clearly related to job platforms and applications: Shopify signup, Workday-based career pages (multiple companies), Randstad applications, Wellfound, Remote.co, Hubstaff Talent. This suggests that our hero #2 was actively searching for remote or international roles, as a front- and back-end developer, but also as a cloud admin and web3 developer.
Portfolio / project activity. We also noticed several accounts on portfolio and CV platforms using several different names: Netlify/Vercel links, a Figma site, portfolio-style domains. This indicates that DevWisdom was trying to improve his visibility by creating fake experienced-developer personas to better apply for jobs and build credibility.
Final words
That will be it for their story. On to the next one...
Infostealers are not just threats - they are powerful cyberdefence and investigation tools. With STEALINT, adversary compromise becomes actionable intelligence: monitoring infostealer infections lets a company detect stolen credentials before they are used, and gives investigators a unique window into the operators themselves.
- Discover the product on stealint.com
- Check the exposure of your domain on the STEALINT platform
Article originally published on the NoxHunt blog - read ZachXBT's full investigation on investigation.io/dprk-itw-breach.