 STEALINT
Unlucky Chucky: uncovering Solonik's personas and origin
For a few months now, a threat actor named Solonik has been actively posting databases on several well-known cybercriminal forums.
We started monitoring this alias on January 12th, when many Instagram users received password-reset emails and, at the same time, an alleged database containing 17 million Instagram user records was posted on a popular cybercrime forum by the user "Solonik" (read the Malwarebytes analysis).
While the alleged database was quickly labelled as an old compilation of Instagram breaches with no freshly dumped data, it brought attention to the Solonik threat actor, who kept actively publishing other databases with alluring names. While doing so, Solonik advertised his Telegram channel, which reached almost 7k followers at its peak.
Note: while we were researching Solonik's activities, StealthMole's experts were quicker than us and published an article explaining their research on the same topic on January 26th. Their article concludes that Solonik used several nicknames such as Chucky and Chucky_lucky, and seems to have ties with Iranian and Persian-speaking Telegram channels.
We initially planned on writing a long article, but considering the heavy work had already been done, we decided to go straight to the point on how we also found Solonik's old aliases, and give new insights found using our investigation capabilities.
Solonik's personas and activities
On his Telegram channel, Solonik posted a screenshot of a message he sent to a BreachForums administrator, about an old alias of his he lost access to and wants to reclaim: Chucky_lucky.
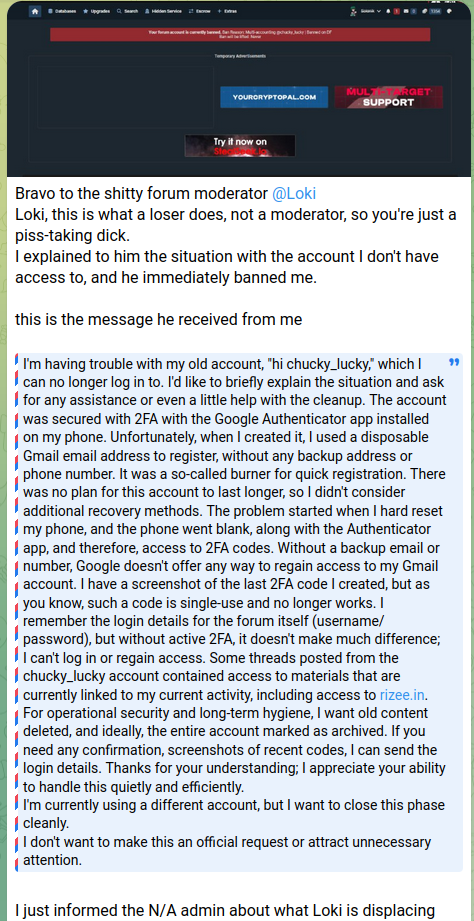
So we have the Solonik = Chucky_lucky link.
In the screenshot, we can also see that he makes a reference to the hack of rizee.in as an "old activity" he now wants to hide. This is interesting: the first thread mentioning this hack was posted on DarkForums on August 20th, 2025, by someone named Chucky_BF. This alias can also be found on BreachForums. We can therefore assume that Chucky_lucky and Chucky_BF are the same person. This is confirmed: in threads posted by Chucky_lucky on BreachForums, archived by our platform, he advertises the Telegram handle t.me/chucky_bf.
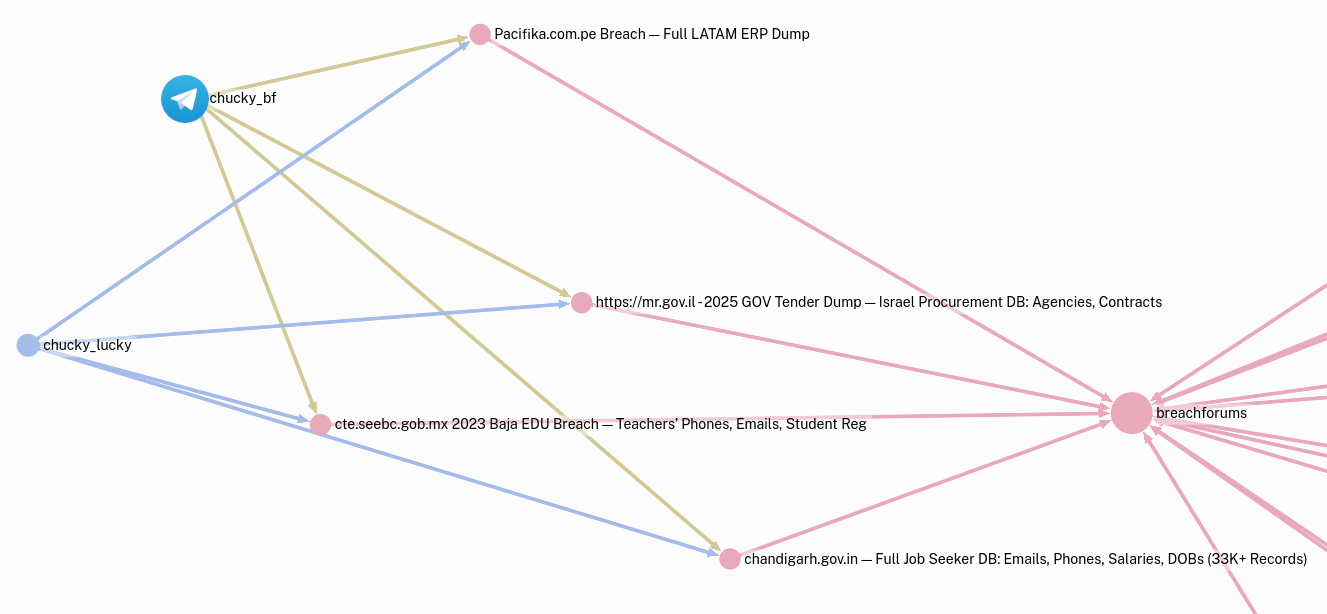
We can now link Solonik to Chucky_lucky and Chucky_BF. The old Chucky_BF alias leads to a lot of activity on cybercriminal forums:
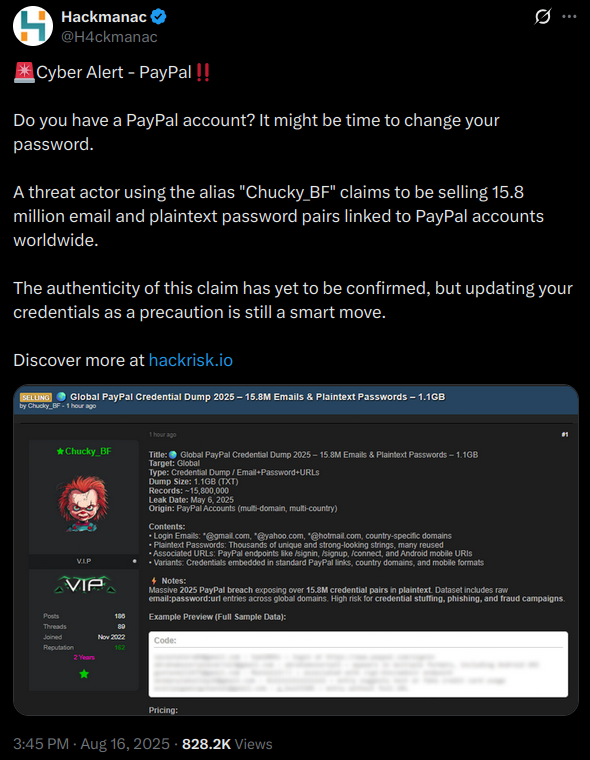
Note that his profile picture, shown in the screenshot above, is the same as the one he used on his Chucky_lucky handle:
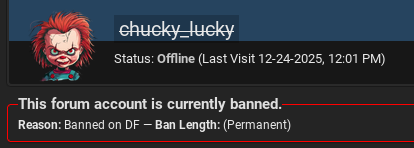
A few more searches later, we found the following thread mentioning another Telegram handle, chucky_leakbasela:
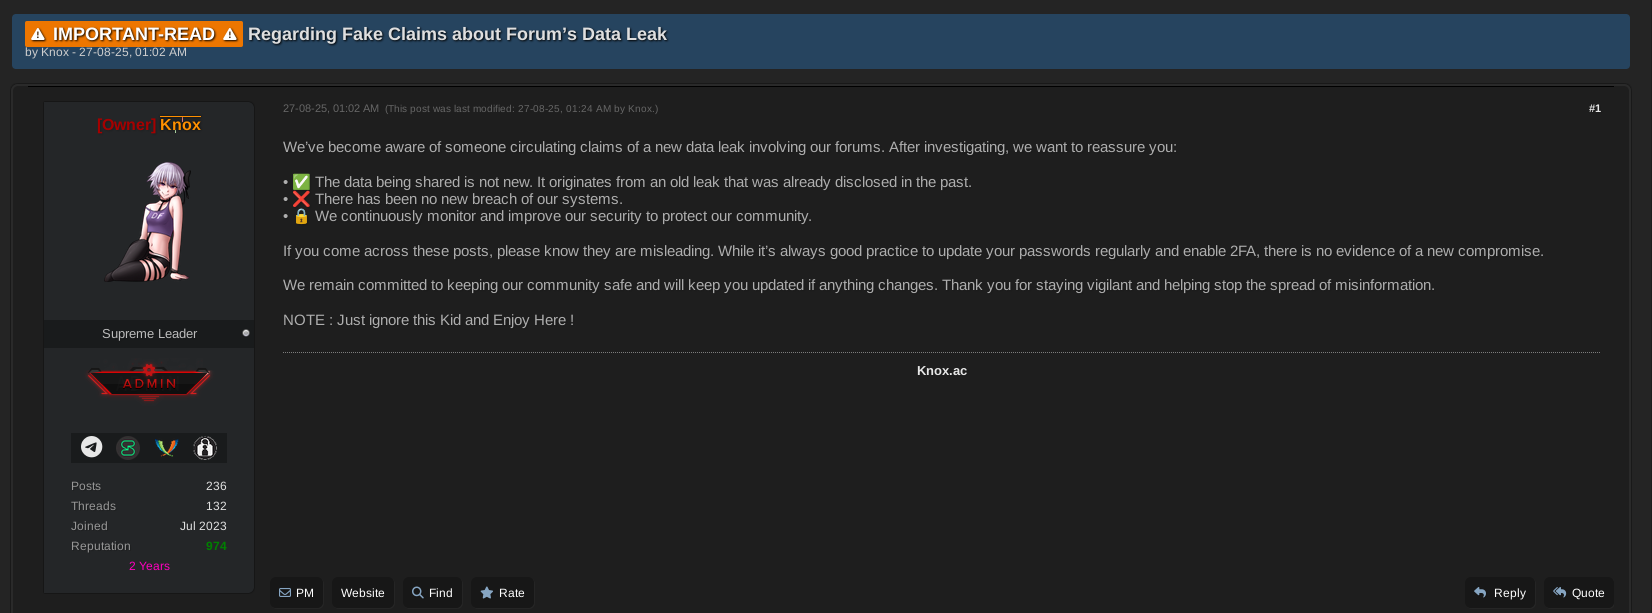
When Chucky got unlucky
Using passive searches, archived forum data and Telegram handle extraction, we were able to retrieve the Chucky* handles used by Solonik. But there is more.
On April 18th, 2025, someone on an Indonesian computer downloaded and executed what appeared to be an infected layededge-bot executable embedding an infostealer. NoxHunt experts were able to retrieve the stolen credentials exfiltrated from this machine. The following account information was saved in the victim's browser:
https://breachforums.vc/member.php : chucky_lucky : ****
https://breachforums.is/member     : chucky_lucky : ****
https://breachforums.st/member     : chucky_lucky : ****
...as well as other accounts on hacking websites with the following logins:
Chucky
andinov
andinov666
icebreaker666
cobaylis
cocacola
Did all of these accounts belong to Solonik over time? Not sure: the passwords associated with these last six accounts are significantly weaker than the ones used for the chucky_lucky accounts, which could either mean:
- that these are very old nicknames used by Solonik a long time ago;
- or that the infected computer is not Solonik's, but one he used occasionally - for example belonging to a member of his family, to a friend, or to an Internet café he went to.
Stolen credentials from stealer data do not come with a date for each entry: they only tell you that the URL:login:password entries belong to the same computer. From there, since the infected computer can be shared, one has to be careful before drawing any conclusion.
Looking at the stolen credentials and the system information, we noticed entries for several accounts on Indonesian official websites, and the system language was Indonesian. Moreover, the location of the external IP address of the computer network also happens to resolve to Indonesia: we can conclude that Solonik is probably from Indonesia.
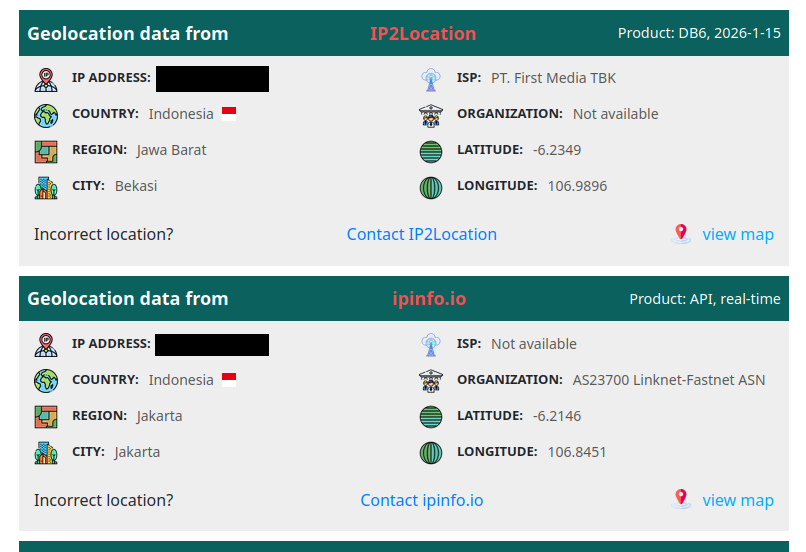
To corroborate some of StealthMole's findings, we did find in the stealer data one account on an Iranian cracking website, which could explain why Solonik has indeed shown some presence on the Iranian hacking scene.
Appendix: Solonik associated threads
DATABASE VIETISO.COM - 209K VIETNAMESE TRAVEL CLIENTS + FULL KYC DATA (2026)
DATABASE HORUSDM.COM.BR - MUNICIPAL TAX SYSTEM DATABASES (BRAZIL, 2M+ RECORDS) 14.01.2026
DATABASE [2026] RMONEYINDIA.COM - INDIAN FINTECH BREACH - 1.5GB SQL
COLLECTION PAKISTAN - PTML CELL TOWER GEOLOCATIONS (5M) | KARACHI BTS GRID
COLLECTION EPSTEIN FILES 2024 - FLIGHT LOGS, BLACK BOOK, US COURT DOCS 2026
DATABASE KNOWMYCUSTOMER.IN - 3.4M CORPORATE LEADS - TATA TELE B2B INDIA
DATABASE TEXTITUTE.COM - SMS & CONTACT PLATFORM + CLIENT DB 13.01.2026
DATABASE COSTCO.COM.TW - 526K TAIWAN CUSTOMERS DATABASE (PII + CREDENTIALS)
DATABASE UNSOED.AC.ID - 42K INDONESIAN UNIVERSITY STUDENT RECORDS + EMAIL, PHONE, ID
DATABASE KAZAKHSTAN - NATIONAL CITIZENS DATABASE (INN, DOB, FULL NAMES)
DATABASE US MILITARY AIRPORTS - FULL COORDINATES & FAA DATA (STRATEGIC SITES)
DATABASE SYSTAGG.COM.BR - 100K FULL BRAZILIAN CANDIDATE PROFILES + CPF + EMPLOY
DATABASE IHEC.IQ - 4.5M IRAQI VOTER RECORDS (FULL ELECTORAL DATA)
DATABASE 321K SEEDS PHARSE ETHERNUM 2026
DATABASE FGTS.GOV.BR - 1.5M BRAZILIAN PENSION RECORDS (FULL CPF + SALARY HISTORY)
DATABASE EPU.EDU.IQ - ERBIL POLYTECHNIC STUDENT & TEACHER RECORDS + FILES
DATABASE IRGC.GOV.IR - 240K IRANIAN REVOLUTIONARY GUARDS (FULL IDENTITY + CONTACT)
DATABASE WA.IRAN - 1.2M WHATSAPP USERS (MOBILE NUMBERS ONLY, 2024)
DATABASE MODHOSPITAL.KR - 45K KOREAN HOSPITAL PATIENT & SYSTEM RECORDS 14.01.2026
DATABASE FUSE.CO.ID - 199K INSURANCE RECORDS + FULL POLICY + KTP/EMAIL/PHONE 2026
DATABASE IRANCELL - NATIONAL TELCO DUMP | 60M CUSTOMERS | .MDB FORMAT
DATABASE IWINV.KR - 144K KOREAN VPS HOSTING USERS + LOGIN (FULL SQL DUMP)
DATABASE ACUITY.COM - 9M ILLINOIS INSURANCE CUSTOMERS
DATABASE FCBB.COM - USA BROKERAGE DATABASE + NDA + LOI + LISTING DOCS (FULL)
DATABASE SNT-RF.RU - 9.9K RUSSIAN NON-COMMERCIAL GARDENING ENTITIES (FULL CORP DUMP)
DATABASE BODOGLIFE.COM - 24.9K US GAMBLING USERS (FULL DATABASE, 2026)
DATABASE LPSE.DEPHUB.GO.ID - 735K+ INDONESIAN GOVT TENDERS & WINNING CONTRACTORS
DATABASE RIZEE.IN - 100K STUDENTS + 14.8M QUESTIONS | Breached 10.01.2026
DATABASE OSSESANJUAN.COM.AR - 98K GOV (ARGENTINA, 2026 DUMP)
DATABASE BTCONNECT.COM - 49.9K UK CRYPTO CLIENT RECORDS (2025 DATABASE LEAK)
DATABASE CHAINLINK.ORG - 6K WEB3 INVESTORS W/ EMAIL + ETH WALLETS + AMOUNTS
DATABASE DUBAI CRYPTO - 104 UAE HNW INVESTORS (FULL EMAIL LIST, 2025)
DATABASE LUMINPDF.COM - 15.4M USERS EXPOSED (EMAIL, HASHES, TOKENS, GENDER, LANG)
DATABASE IRAN TELCO DATASET - FULL PII DUMP (ICCID, ID, ADDR, GSM)
DATABASE KPS.KU.AC.TH - THAI UNIVERSITY SERVER SQL DUMP (AGRICULTURE + ECOM) 8 JAN 2026
DATABASE CHINA CITIZEN DATABASE - 1.2B RECORDS WITH NAMES, IDS, GPS, MOBILE
[SALE] mail.gdt.gov.vn OWA Access – Vietnam Tax Authority Employee Mailbox
Appendix: Chucky_lucky latest threads
cte.seebc.gob.mx 2023 Baja EDU Breach - Teachers' Phones, Emails, Student Reg
Pacifika.com.pe Breach - Full LATAM ERP Dump
https://mr.gov.il - 2025 GOV Tender Dump - Israel Procurement DB: Agencies, Contracts
chandigarh.gov.in - Full Job Seeker DB: Emails, Phones, Salary
Final words
Solonik is an enigmatic actor that was, at some point in time, one of the most prolific posters on Breach and DarkForums. Though, most of that was smoke and mirrors: threads with alluring titles but old, recompiled data, attempts at selling publicly available content... After a few weeks in the spotlight, almost all Solonik activities have now been wiped: forum threads got deleted, profiles got banned, as well as his Telegram channels.
What can be learned from this quick investigation?
- Archiving cybercriminal platforms' content is key to keep track of actors.
- Tracking messaging handles helps make historical links: threat actors change public aliases often, but more rarely their contact handles.
- Cybercriminals install a lot of cracked software and are not immune to stealers! Stealer data gathering can give you exclusive insights.
At NoxHunt, we do all that! If you are interested in cybercriminal tracking, protect your own perimeter too: discover STEALINT and check your domain's exposure on the platform.
Article originally published on the NoxHunt blog, February 11th 2026.